Black Friday is just around the corner, and this is the time to make sure your Magento checkout is secure, stable, and ready for increased traffic.
Today we're releasing Firecheckout 1.37, bringing important security fixes across several checkout modules and introducing Checkout Doctor, a new tool that helps merchants identify checkout problems before they turn into lost orders.
There are also important PHP and Nginx security updates that Magento store owners should review.
Firecheckout 1.37: Important Security Fixes
Security remains one of our top priorities. Following our October security review, we've continued auditing our modules and improving their protection.
Firecheckout 1.37 addresses a high-severity security issue in the Checkout Success module, strengthening access controls for success page previews and administrative settings.
The release also includes additional security improvements across several modules:
- Checkout Registration: Stronger server-side password validation.
- Checkout Fields: Improved authorization and input validation.
- Order Attachments: Stronger file validation and access protection.
- Address Validation: Improved output escaping and validation request handling.
- Delivery Date: Stricter validation of delivery dates and times.
- Checkout Consumer Rights: Additional protection for order withdrawal requests.
We've also improved the security of inline scripts and made several compatibility and stability fixes.
We strongly recommend updating to Firecheckout 1.37, especially if your store uses any of the affected modules.
You can find the complete list of changes in the Firecheckout changelog.
Meet Checkout Doctor: Stop Losing Revenue to Hidden Checkout Errors
A checkout can look perfectly fine while customers struggle to complete their orders.
A payment request fails, a JavaScript error blocks the checkout button, or a shipping method stops working. Customers often don't report these problems. They simply leave and buy somewhere else.
And unless someone investigates the logs, these issues can remain unnoticed for days or even weeks.
That's why we've developed Checkout Doctor, a new Magento 2 module included with Firecheckout 1.37.
Its purpose is simple: help you understand what's happening during checkout, find problems faster, and reduce lost revenue.
Know Your Checkout Health
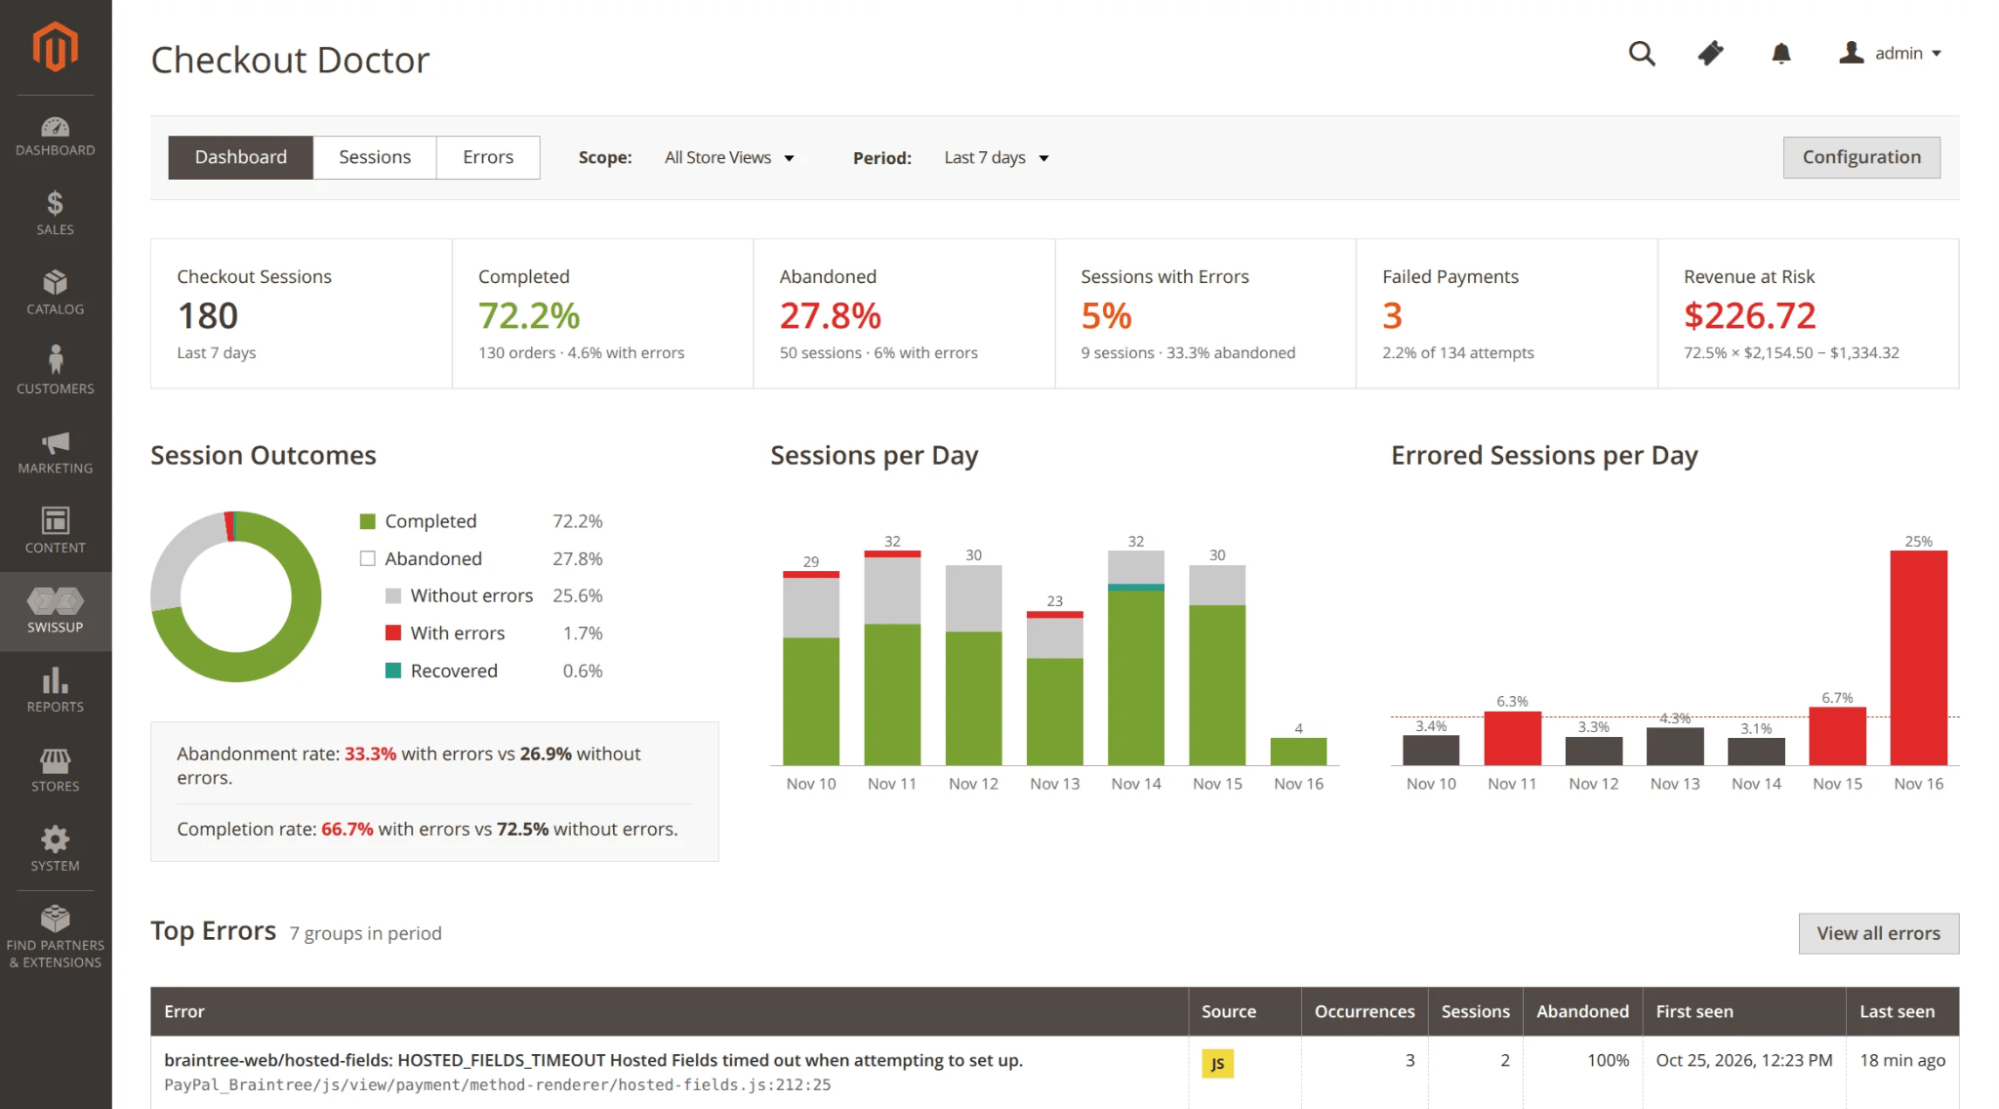
Checkout Doctor introduces a dashboard showing how your checkout performs in real customer sessions.
You can monitor completed and abandoned checkouts, failed payment attempts, sessions affected by errors, and the most common problems customers encounter.
It also estimates revenue at risk by comparing sessions with checkout problems against sessions that completed without them.
This helps you understand not just how many errors occur, but how much revenue those problems could be costing your business.
Find Out Why Customers Can't Complete Their Orders
Every checkout session has a timeline showing the steps a customer took, from entering their address and choosing a shipping method to attempting payment.
Checkout Doctor records JavaScript errors, PHP errors, failed payment attempts, and other checkout problems.
It can also identify signs of customer frustration, such as repeatedly clicking a button that doesn't respond.
Instead of guessing why a customer abandoned checkout, your developers can examine the session timeline, error details, and available backtraces to investigate what went wrong.
Catch Problems Before They Become Bigger
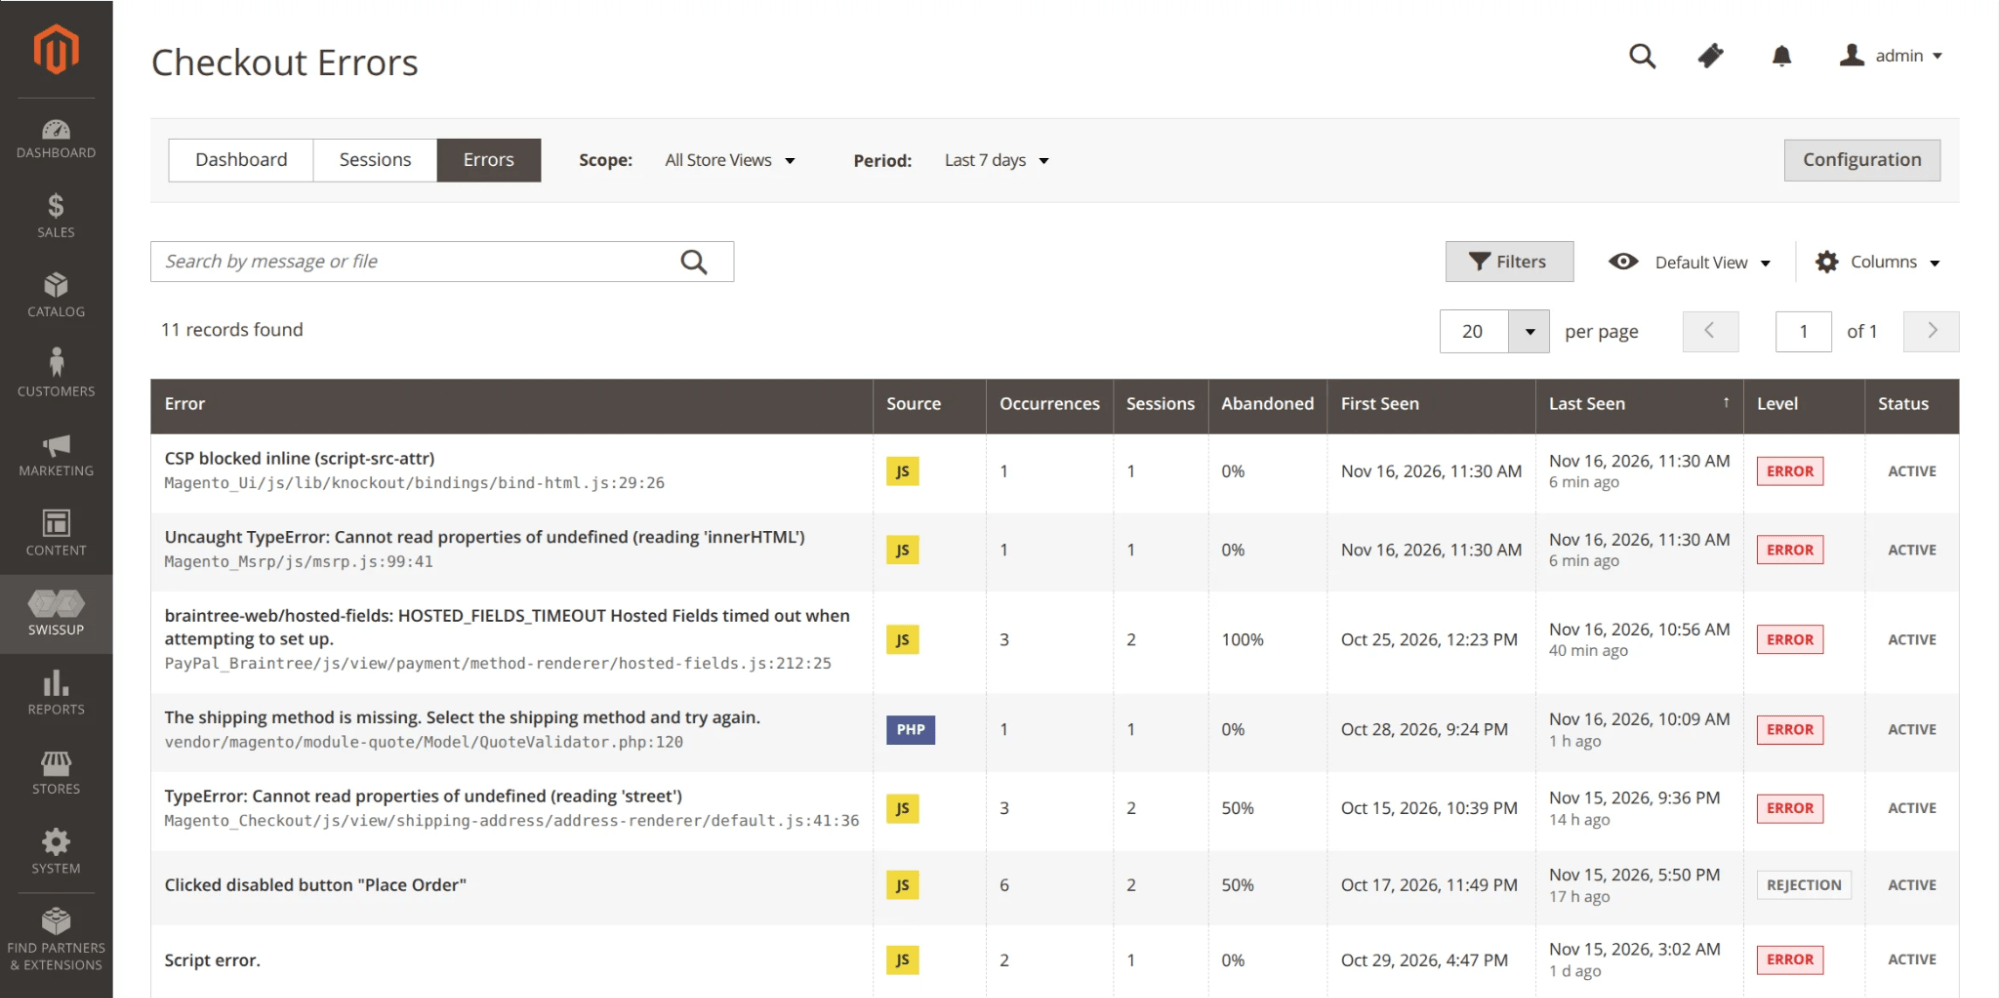
Not every checkout error is critical, but even small recurring issues can affect conversions.
Checkout Doctor helps you identify frequent problems, investigate affected sessions, and filter out known harmless errors. It can also display an alert in Magento Admin when the percentage of checkout sessions with errors exceeds your configured threshold.
Checkout Doctor is included with Firecheckout 1.37 and is also available as a standalone extension.
Learn more in the Checkout Doctor documentation.
Important PHP and Nginx Security Updates
Firecheckout isn't the only software that needs attention this month. Two important security announcements also affect technologies commonly used by Magento stores.
PHP Security Updates — November 19, 2026
The PHP development team has released security updates for all supported PHP branches, addressing vulnerabilities that include issues rated Critical.
The highest-severity issues require non-default configurations or uncommon setups, but all affected users are encouraged to update.
The new security releases are:
- PHP 8.2.36
- PHP 8.3.37
- PHP 8.4.28
- PHP 8.5.13
We recommend checking your server's PHP version and applying the latest security patches compatible with your Magento installation.
Read the official PHP security announcement.
Nginx HTTP/2 Security Vulnerability
A serious Nginx security vulnerability, CVE-2026-123007, was also disclosed on November 18.
The issue affects Nginx servers with HTTP/2 enabled and can potentially allow unauthenticated attackers to execute code under vulnerable conditions.
The vulnerability has been fixed in Nginx 1.30.7 and 1.31.9.
If your Magento store runs on Nginx, we recommend contacting your hosting provider or system administrator to confirm that the necessary security fixes have been applied. Some hosting providers may deliver backported fixes without changing the reported Nginx version.
Read the official Nginx security advisory.
Black Friday: Is Your Magento Checkout Ready?
Black Friday brings more visitors, more orders, and more pressure on your checkout.
A problem that normally affects only a few customers can become much more expensive during peak sales.
Before the shopping rush begins, we recommend checking a few essential things:
- Update Firecheckout and other Magento extensions to their latest secure versions.
- Apply available Magento, PHP, and Nginx security patches.
- Test guest checkout, payment methods, shipping options, and discount codes.
- Enable Checkout Doctor and review recent checkout errors.
- Investigate failed payments and recurring checkout problems.
Don't wait for customer complaints to discover that your checkout is broken.
Even a short checkout health review before Black Friday can help you catch problems that might otherwise go unnoticed.
How to Update Firecheckout 1.37
Customers With Active Support and Updates
You can update Firecheckout through Composer using your existing SwissUpLabs subscription.
We recommend performing the update on a staging environment first and testing your checkout before deploying to production.
If you use the Swissup Module Manager, you can also check for available updates directly in Magento Admin.
See our Firecheckout upgrade instructions.
Customers Without Active Support
If your support and updates subscription has expired, you can still request security fixes for affected modules.
Simply contact our support team using the account associated with your original purchase, and we'll provide the necessary standalone security patches on request.
Alternatively, you can renew your subscription to access Firecheckout 1.37, Checkout Doctor, and future updates.
Keep Your Checkout Secure and Healthy
A reliable checkout is essential for every ecommerce business. Security vulnerabilities can put your store at risk, while unnoticed technical problems can quietly cost you sales.
With Firecheckout 1.37, we're addressing both sides: improving checkout security and introducing Checkout Doctor to help merchants understand and improve checkout health.
Update your Firecheckout, check your server security, and make sure your store is ready for Black Friday.
Every successful checkout matters.